Qilin puts Argentine Army on leak site
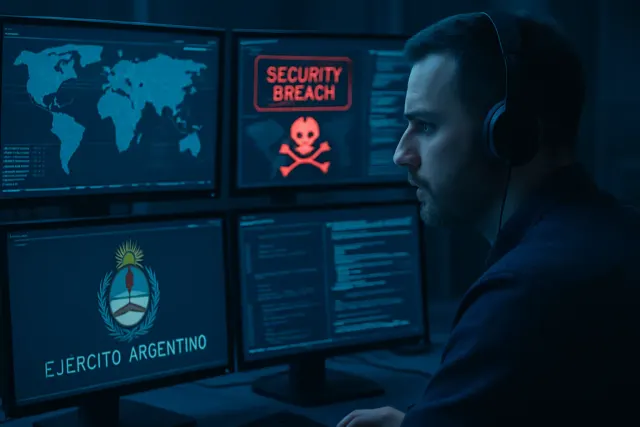
Qilin added the Argentine Army to its leak site and tied it to a claimed July 24 attack. Signs of credential theft also emerged.
Qilin added the "Argentine Army" to its leak site on July 24, 2026. IntelFusions says the listing is unverified and appears meant to pressure the alleged target, not confirm a breach. At the same time, Dexpose said the group publicly claimed an attack on the official Argentine Army domain, argentina.gob.ar/defensa/ejercito, while Ransomware.live flagged infostealer activity on associated accounts and more than 200,000 compromised users.
Qilin added the "Argentine Army" to its leak site on July 24, 2026, in an unverified leak-site entry that IntelFusions describes as a pressure tactic, not a confirmed breach. Dexpose, Ransomware.live and IntelFusions connect the case to an attack claimed that same day and to signs of credential compromise.
What is known about the case?
Dexpose reported that on July 24, 2026, Qilin publicly claimed an attack against the Argentine Army’s official domain, argentina.gob.ar/defensa/ejercito, and threatened to expose sensitive military data. That post lines up in time with the listing seen on the leak site.
Ransomware.live, meanwhile, shows a specific "Argentine Army" entry attributed to Qilin, discovered the same day, July 24. The entry references the Army’s official domain and points to infostealer activity on associated accounts, which suggests at least credential compromise, even though the main intrusion has not been verified.
The same source estimates that the entry tied to Qilin corresponds to an attack dated July 24, 2026, and lists more than 200,000 users compromised in related infostealer activity. That volume points to a high risk of credential reuse and a possible access vector for ransomware operators.
What is the context around Qilin activity?
IntelFusions logged 27 listings on Qilin’s leak site between July 22 and 25, within a trend of roughly 120 claims over the last month. In that context, the Argentine Army case appears amid a period of elevated global activity by the group.
The same publication describes Qilin, also known as Agenda, as a ransomware-as-a-service operation active since 2022. Its model combines a core team that maintains the encryptor and leak-site infrastructure, while affiliates carry out intrusions in exchange for a share of the ransom.
IntelFusions adds that Qilin is known for targeting VMware ESXi virtualization servers and links it to the 2024 incident that disrupted blood analysis services at hospitals in London. That background helps frame the type of environment the group typically exploits.
What is the situation in Argentina?
Over the last 12 months, IntelFusions recorded 62 ransomware leak-site claims against Argentine organizations, spread across 17 different groups. The figure suggests the real number of victims in the country may be higher than what appears in narrower panels such as Pulse.
Ransomware.live also tracks between 169 and 174 victims attributed to Argentina in its interactive map, well above the 10 recent victims visible in the Pulse panel. For the local ecosystem, that indicates activity against Argentine organizations has been more widespread over time and across more groups than some partial datasets show.
RansomLook, meanwhile, records more than 32,000 ransomware posts since 2022 and places Qilin among the most active groups, with 14.9% of posts in its recent sample and an increase of more than 200% over the past week. The Argentine Army case lands within that global surge in activity.
Sources
- Ransomware Wing — víctimas, grupos y patronespulse.kalir.io· Pulse
- La llegada de los “cárteles” a la ciberseguridadinversorlatam.com· Inversor Latam
- Qilin ransomware lists Argentina's army on its leak siteintelfusions.com· IntelFusions
- Victim: Ejército Argentinoransomware.live· Ransomware.live
- Ransomware.live 👀 — Map ARransomware.live· Ransomware.live
- RansomLook — Open ransomware intelligenceransomlook.io· RansomLook
- Qilin Ransomware Group Targets Ejército Argentinodexpose.io· Dexpose