Brazil Accounts for 601 Ransomware Victims
Brandefense/ATLAS logged 601 Brazilian organizations on leak sites, with technology, consulting, education, government and retail most exposed.
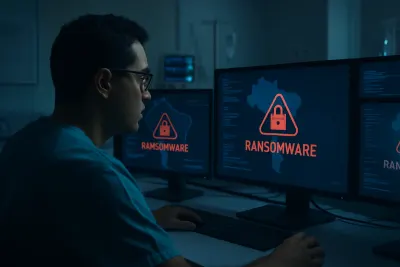
Brandefense/ATLAS logged 601 Brazilian organizations listed as ransomware victims on leak sites. Consulting, education and research, technology, government and public sector, and retail were among the most represented industries.
Update November 1, 2026: This note adds the regional count of 1,080 ransomware victims in Latin America and the Caribbean, with 31.3% in critical infrastructure, and new technical findings on n0n, including confirmed victims, targets, and tactics.
Brandefense/ATLAS recorded 601 organizations in Brazil listed as ransomware victims on leak sites. The monitoring places consulting, education and research, technology, government and public sector, and retail among the most represented sectors. Among the groups with Brazilian victims are LockBit, The Gentlemen, and RansomHub, according to the dashboard reviewed on October 29, 2026.
What do the records show about Brazil?
ATLAS also documented recent activity that places Brazil at the center of several ransomware profiles. In September 2026, Brandefense recorded 24 victims listed in the country, equal to 2.8% of the global victims observed during that period. The figure comes from leak-site monitoring and claims posted by the groups themselves.
In the recent-victim sample, ATLAS listed Partido Liberal, claimed by Whitearmor; GTL Concreto e Logística and MPI LTDA, claimed by Emperador; Prafesta, claimed by N0n; Hospital Sírio-Libanês, claimed by The-seven-deadly-sins; and Universidade de Passo Fundo and CLIMEDI, claimed by The Gentlemen. The records include nonprofit organizations, manufacturing, construction, health care, and education and research.
What does ATLAS say about Arcus Media and N0n?
ATLAS identified Brazil as the country with the highest share of Arcus Media victims, a ransomware-as-a-service group that uses double extortion. The source documents the use of ChaCha20 encryption plus RSA-2048 and points to victims in manufacturing, health care, retail, and business services. In Brazil, technology was the most represented sector, followed by manufacturing, consulting, education and research, and retail.
In N0n's case, ATLAS described techniques tied to access through Remote Desktop Protocol and valid accounts, execution through commands, persistence through autostart, obfuscation, data staging, recovery inhibition, data encryption, and service stoppage. Brazil accounted for 53.4% of the victims listed by the group in the profile reviewed.
What other victims and tactics appear in the monitoring?
ATLAS also recorded Eclipse with a Brazilian retail victim, dipecarr.com.br, posted on October 8, 2026. At the same time, other coverage of N0n described it as an emerging extortion group first detected on September 18, 2026, with affected organizations in Brazil and other countries.
Cyberint described it as a financially motivated actor focused on data theft and extortion. According to that observation, no file encryption had been seen and the leak-site claims referred to stolen data only. The report counted 120 victims in 28 countries as of October 19, 2026, and ransom demands ranging from $2.4 million to $25 million.
Mallory, in a report attributed to SOCRadar findings from an exposed workspace used by N0n operators, mentioned attack scripts, cipher code, extortion infrastructure, and an AI-assisted coding environment. It also warned that four of 23 organizations involved showed only access attempts with no proven success. Cyware, for its part, reported credential stuffing, data exfiltration, and encryption, along with indicators such as the directory C:\Users\Public\n0n\ and files with the .n0n extension.
What does the new regional report add?
Coverage citing FortiRecon data reported 141 confirmed ransomware victims in Brazil, 69 in Mexico, 50 in Argentina, and 41 in Colombia during 2025. Regionally, the critical infrastructure report cited by Diario Financiero counted 1,080 ransomware victims in Latin America and the Caribbean between January 2025 and September 2026, with 31.3% of cases in critical infrastructure.
In that regional tally, the sectors with the most identified organizations were government, with 81; health care, with 78; and transportation and logistics, with 68.
What does the investigation add on n0n?
Cyberint reported that n0n had 120 listed victims across 28 countries as of October 19, 2026, although it said no file encryption had been observed and that leak-site posts referred only to stolen data. The observed ransom demands ranged from $2.4 million to $25 million.
SOCRadar identified at least 23 organizations involved in n0n's extortion operation across 14 countries, including an Argentine ministry and a Venezuelan internet service provider. An analysis based on those findings also said n0n used credential stuffing against 305 FortiGate SSL-VPN devices and sought exposed RDP services. That count distinguished between 93 victims posted on the leak site and 23 confirmed target organizations from the investigation.
SOCRadar said an exposed workspace linked to n0n contained attack scripts, cipher code, extortion infrastructure, and an artificial intelligence-assisted programming environment. Four of the 23 organizations showed only access attempts with no proven success, according to that analysis. SecurityArsenal added initial-access techniques through edge devices or VPN, script and macro execution, lateral movement with PsExec/WMI, and data preparation before encryption, including shadow copy deletion, mass enumeration, and staging.
What is known about The Gentlemen?
A technical profile of The Gentlemen identified techniques including propagation through Group Policy and linked the actor to the names Storm-2697, according to Microsoft, and GOLD SHERWOOD, according to Sophos. That material provides general context on the actor, but does not confirm its responsibility for the Oldelval incident.
Sources
- n0n Ransomware: Inside an AI-Assisted Extortion Operationsocradar.io· SOCRadar
- The Gentlemen Ransomware: Tactics, GPO Spread, Defencesnhimg.org· NHIMG
- Ransomware LATAM 2026: alza del 25,5% y cómo actuarblog-es.lac.tdsynnex.com· TD SYNNEXUnverified URL
- n0n Ransomware Group Spends $7K on AI Tools, Then Leaves Its Own Server Wide Opencryptobriefing.com· Crypto Briefing
- Eclipse Ransomware: Victims, TTPs & IOCsatlas.brandefense.io· Brandefense ATLAS
- Ransomware in September 2026: 857 Victimsbrandefense.io· Brandefense
- Exposed n0n Ransomware Workspace Reveals AI-Assisted, Credential-Based Extortionmallory.ai· Mallory
- La última vuelta de tuerca del ransomware: sin backups no hay rescateescudodigital.com· Escudo Digital
- Threat Actor Investigation n0ncyberint.com· Cyberint
- Cyware Daily Threat Intelligence - October 28, 2026cyware.com· Cyware
- Ransomware Attacks in Brazil: Victims & Groupsatlas.brandefense.io· Brandefense ATLAS
- Arcus Media Ransomware: Victims, Targets & Activityatlas.brandefense.io· Brandefense ATLAS
- N0n Ransomware: Victims, TTPs & IOCsatlas.brandefense.io· Brandefense ATLAS
- Fortinet registró cerca de 15.000 millones de intentos de explotación en América Latina durante 2025tabulado.net· Tabulado.net
- México registró 60 víctimas de ransomware en infraestructura críticaes-us.noticias.yahoo.com· Noticias Yahoo
- Ransomware in September 2026: 857 Victimsbrandefense.io· Brandefense
- N0N Ransomware Gang Claims 20 New Victims — Sector Targeting Analysis & Detection Rulessecurityarsenal.com· SecurityArsenal
- RANSOMWARE: Los ataques ya no solo secuestran datos, ahora amenazan la continuidad de las empresasportalinnova.cl· Portal Innova